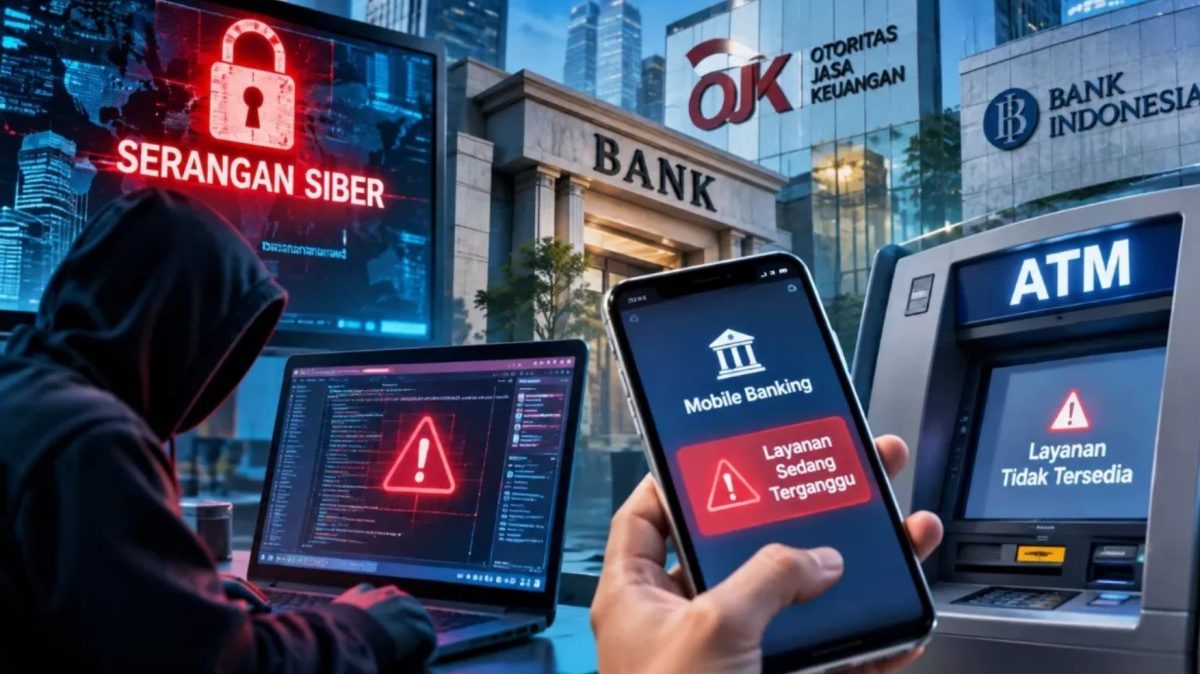
Banda Aceh News | JAKARTA — Recent technical disruptions and security incidents across international banking networks have reignited urgent policy discussions concerning the absolute resilience of digital financial infrastructure. In Indonesia, public concern escalated sharply following threat intelligence reports released by FortiGuard Labs on November 7, 2026, which recorded roughly 350,600 cyber threat activities nationwide, with the financial sector emerging as the primary target.
Industry analysts emphasize that raw threat metrics do not equate to successful bank account breaches. The detected telemetry encompasses routine network scanning, aggressive probing attempts, sophisticated malware payloads, and anomalous traffic patterns.
Nevertheless, the heavy targeting of the financial services sector underscores the pressing necessity to harden the national banking architecture against systemic cyber incursions.
Parallel warnings emerged from European cyber threat intelligence firm ThreatFabric, whose research uncovered a specialized Android banking trojan designated as Hirudo. The malware specifically targets eight Indonesian mobile banking applications distributed across seven major domestic institutions.
Hirudo is engineered to harvest user credentials, intercept multi-factor authentication SMS messages, capture personal identification numbers (PINs), and commandeer infected user handsets. While the total volume of compromised victims in Indonesia remains undisclosed and there is no direct empirical link between the Hirudo trojan and the 350,000 FortiGuard-detected threat instances, the discovery highlights growing exposure to advanced mobile endpoint threats.
Global Outages and Domestic Operational Pressures
Vulnerabilities within contemporary financial ecosystems extend far beyond malicious cyber attacks, as demonstrated by recent high-profile system failures across global markets.
In Japan, 128 cooperative credit institutions—known as Shinkin Banks—suffered debilitating operational outages affecting automated teller machines (ATMs), interbank clearing, and internet banking services due to telecommunications hardware failures at their central processing hub. The incident was rooted in physical infrastructure decay rather than external hacking.
Concurrently, in Malaysia, the official portal of Bank Rakyat suffered a visual defacement following a security compromise originating from a third-party vendor server. Meanwhile, in France, Crédit Mutuel Arkéa reported financial losses totaling approximately 100 million euros stemming from fraudulent transactions currently under active investigation by law enforcement authorities.
Domestically, Indonesia has also experienced localized operational strain. MNC Bank recently confronted digital service disruptions, triggering widespread customer complaints regarding transaction bottlenecks and liquidity withdrawal difficulties.
The Financial Services Authority (OJK) confirmed that it launched an immediate examination into MNC Bank’s liquidity buffers, cash flow management, and legal capacity to meet customer obligations, while explicitly instructing management to settle all outstanding client entitlements. Regulators noted that the operational disruption has not been linked to cyber intrusions, and routine liquidity audits do not automatically signify systemic insolvency.
The Dangers of Shared Technological Dependency
Beneath these isolated operational incidents lies a profound structural vulnerability: the modern banking sector’s deep reliance on shared technological infrastructure. Core payment rails such as BI-FAST, shared ATM switching networks, centralized data centers, third-party telecommunications providers, and software vendors form the invisible backbone of national commerce.
While this interconnectedness drives unprecedented operational efficiency, it introduces severe concentration risks. A catastrophic failure in a single critical node can cascade rapidly across multiple commercial banks, even if individual core banking systems remain unbreached.
In response to these systemic exposures, industry watchdogs—including the OJK, Bank Indonesia (BI), and the National Cyber and Crypto Agency (BSSN)—face mounting pressure to mandate that all banking entities maintain redundant secondary data centers, alternative routing channels, independent security audits, and rigorously tested disaster recovery protocols.
Regional institutions, including Bank Aceh Syariah and other regional development banks (BPD), cannot remain insulated from these systemic realities, as the security of local mobile applications, ATM networks, and municipal transaction portals forms an indispensable pillar of regional economic stability.
While investigators have found no evidence linking the 350,000 detected threat payloads, the MNC Bank disruption, and international banking failures to a unified coordinated operation, financial regulators must confront a fundamental question: Is the shared infrastructure upholding Indonesia’s economy robust enough to survive the catastrophic failure of a single critical system?
In the digital economy, the ultimate threat to commercial banking is not merely illicit capital theft; it is the sudden paralysis of public access to liquidity, which poses an existential danger to public trust and national economic continuity.